Best Compliance Audit Software in 2026: 8 Tools Compared

How we put this together: we compare official feature and pricing pages, app store listings, privacy policies and public user reviews. Prices change, so check the provider's site before you pay.
Key takeaways
- Vanta and Drata suit tech companies seeking SOC 2, ISO 27001, HIPAA, and similar frameworks with automated evidence.
- Secureframe and Sprinto suit startups that want guided workflows at a lower starting scope.
- AuditBoard suits larger firms that need SOX, internal audit, and enterprise risk in one program.
- LogicGate and Hyperproof suit firms that need flexible multi-framework governance rather than a single-framework tool.
Quick comparison
| Name | Who it suits | Starting price | Free option | |
|---|---|---|---|---|
 Vanta | Automated SOC 2 and ISO readiness | See website | No | Visit |
 Drata | Automated compliance with guided workflows | See website | No | Visit |
 Secureframe | Guided SOC 2 for startups | See website | No | Visit |
 AuditBoard | Enterprise SOX and internal audit | See website | No | Visit |
 LogicGate | Flexible multi-framework GRC | See website | No | Visit |
 Hyperproof | Multi-framework evidence and controls | See website | No | Visit |
 Sprinto | Startup compliance at lower scope | See website | No | Visit |
 Thoropass | Compliance plus in-house audit support | See website | No | Visit |
The best compliance audit software
We compared compliance audit software and tools on framework coverage, evidence automation, audit workflow, integrations, and price transparency. The eight options below cover automated SOC 2 and ISO readiness for tech companies, plus enterprise governance, risk, and internal audit programs. Note that a platform prepares you for an audit, while an independent auditor performs the audit and issues the report.
Vanta suits a tech company that needs to get audit-ready for SOC 2, ISO 27001, HIPAA, or similar frameworks. It fits automated soc 2 and iso readiness well, and it is worth shortlisting if that description matches your situation.
It connects to cloud and business systems, collects evidence automatically, and monitors controls continuously, so gaps appear before an audit, not during it. That strength matters most when the team reviewing the bill is not the same team running the system, because both groups need the same numbers in plain form.
The catch is total cost: the platform price does not include the independent audit, pentest, or implementation help, so budget for those separately. Before you commit, ask for a trial on your own data, check how support responds, and confirm what happens when you outgrow the entry tier.
- Automated evidence collection
- Many integrations
- Continuous control monitoring
- Quote-based pricing
- Audit itself is billed separately by an auditor
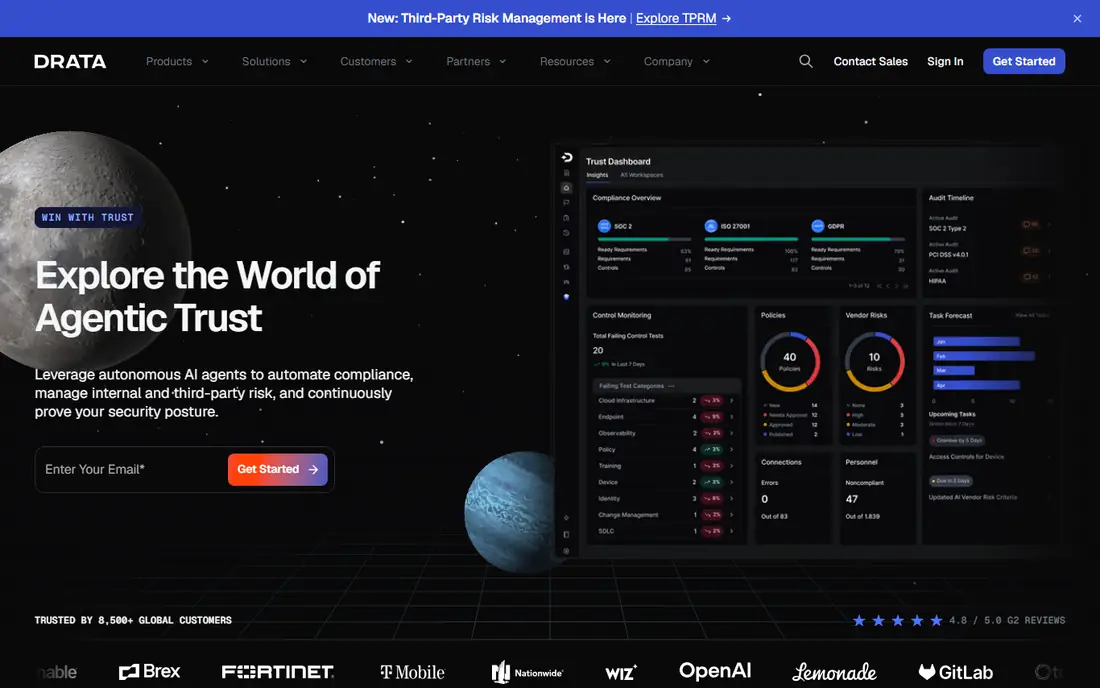
Drata suits a growing company that wants structured compliance workflows plus automated evidence. It fits automated compliance with guided workflows well, and it is worth shortlisting if that description matches your situation.
Its framework templates and monitoring help teams move from scattered spreadsheets to a repeatable control program. In day to day use, the value shows up in fewer surprises, clearer ownership, and less time spent chasing down why a number moved.
The catch is scope pricing: each added framework and service can raise the total, so confirm the price for all frameworks you need in year one. Before you sign, test it with a small group, read the renewal terms, and confirm the features you need are in the plan you are buying, not a higher tier.
- Automated evidence and control monitoring
- Framework templates
- Auditor connections
- Quote-based pricing
- Added frameworks increase cost
Secureframe suits a startup that wants guided steps through a first SOC 2 or ISO program. It fits guided soc 2 for startups well, and it is worth shortlisting if that description matches your situation.
Its workflows explain what to do next, which helps a small team without a dedicated compliance lead. For a busy team, the practical benefit is less manual work and a clearer record of what changed and why.
The catch is depth: larger firms with complex risk and internal audit needs may need a broader GRC platform alongside it. Before you commit, run a short pilot, compare the total cost with add-ons included, and check how easy it is to export your data later.
- Guided compliance workflows
- Automated evidence
- Audit support connections
- Quote-based pricing
- Audit itself is separate
AuditBoard suits a larger firm that needs SOX compliance, internal audit, and risk management in one connected program. It fits enterprise sox and internal audit well, and it is worth shortlisting if that description matches your situation.
Its workflows link risks, controls, tests, and issues, which helps audit teams work from one record rather than many spreadsheets. That strength matters most when the team reviewing the bill is not the same team running the system, because both groups need the same numbers in plain form.
The catch is scale: pricing and implementation suit enterprises, and a small startup seeking only SOC 2 may find it heavier than needed. Before you commit, ask for a trial on your own data, check how support responds, and confirm what happens when you outgrow the entry tier.
- SOX and internal audit workflows
- Risk and controls management
- Enterprise reporting
- Quote-based enterprise pricing
- Implementation suits larger firms
LogicGate suits a firm that needs to map controls across several frameworks without forcing every team into one rigid template. It fits flexible multi-framework grc well, and it is worth shortlisting if that description matches your situation.
Its flexible workflows let compliance, risk, and audit teams build processes that match how they actually work. In day to day use, the value shows up in fewer surprises, clearer ownership, and less time spent chasing down why a number moved.
The catch is setup: flexibility means configuration time, so buyers should plan for design and testing before rollout. Before you sign, test it with a small group, read the renewal terms, and confirm the features you need are in the plan you are buying, not a higher tier.
- Flexible GRC workflows
- Risk and control mapping
- Multi-framework support
- Quote-based pricing
- Flexibility needs configuration time
Hyperproof suits a team that manages several frameworks and wants evidence reused across them. It fits multi-framework evidence and controls well, and it is worth shortlisting if that description matches your situation.
Its control mapping avoids collecting the same evidence twice for SOC 2, ISO, and HIPAA, which saves time as frameworks stack up. For a busy team, the practical benefit is less manual work and a clearer record of what changed and why.
The catch is scale: it is a strong mid-market GRC pick, but the largest enterprises may need the broader suite depth of AuditBoard. Before you commit, run a short pilot, compare the total cost with add-ons included, and check how easy it is to export your data later.
- Control mapping across frameworks
- Evidence automation
- Audit collaboration
- Quote-based pricing
- Smaller vendor than Vanta or AuditBoard
Sprinto suits a startup that wants automated compliance checks at a scope that fits a first framework. It fits startup compliance at lower scope well, and it is worth shortlisting if that description matches your situation.
Its templates and checks help a small team get audit-ready without hiring a full compliance team first. That strength matters most when the team reviewing the bill is not the same team running the system, because both groups need the same numbers in plain form.
The catch is growth: as frameworks and headcount grow, buyers should confirm how pricing and features scale. Before you commit, ask for a trial on your own data, check how support responds, and confirm what happens when you outgrow the entry tier.
- Automated compliance checks
- Framework templates
- Auditor partner connections
- Quote-based pricing
- Audit itself is separate
Thoropass suits a company that wants compliance software and audit support in one contract. It fits compliance plus in-house audit support well, and it is worth shortlisting if that description matches your situation.
Its model combines platform workflows with audit services, which can simplify planning for a first SOC 2. In day to day use, the value shows up in fewer surprises, clearer ownership, and less time spent chasing down why a number moved.
The catch is contract clarity: buyers should confirm exactly which audit services, frameworks, and fees are included before signing. Before you sign, test it with a small group, read the renewal terms, and confirm the features you need are in the plan you are buying, not a higher tier.
- Compliance platform plus audit services
- Framework guidance
- Evidence workflows
- Quote-based pricing
- Audit scope must be confirmed in the contract
How we picked these
We compared official product pages, pricing pages, and public documentation, and we checked that each homepage loads and matches the product named. We favoured platforms that are actively sold in 2026, that cover recognised frameworks, and that explain evidence automation and audit workflow plainly. Most vendors in this group do not publish list prices, so we wrote See website for every starting price rather than repeating a third-party estimate as a list price. Audit fees, pentests, and implementation are usually separate costs.
How to choose compliance audit software without a failed audit
Start with the framework your customers or regulators actually require, since SOC 2, ISO 27001, HIPAA, SOX, and PCI DSS need different evidence and controls. Next, check integrations with the systems that hold your evidence, such as cloud, identity, HR, and ticketing tools, because manual evidence collection defeats the purpose of automation. Ask whether the platform includes audit support, or only prepares you for an independent auditor, and get audit, pentest, and renewal costs in writing. Test control mapping if you need several frameworks, since reusing evidence across frameworks saves real time. Finally, confirm evidence export and access controls, since your audit record must remain usable if you change vendors.
Frequently asked questions
What is the best compliance audit software?
The best compliance audit software depends on your framework and size. Vanta and Drata lead for automated SOC 2 and ISO readiness, Secureframe and Sprinto suit startups, and AuditBoard leads for enterprise SOX and internal audit.
Which compliance audit software is top rated for SOC 2?
Vanta, Drata, Secureframe, Sprinto, and Thoropass are all strong SOC 2 options in this group. Shortlist by team size, framework count, and whether you want audit support bundled or handled by a separate auditor.
What are the best compliance audit tools for enterprises?
AuditBoard, LogicGate, and Hyperproof suit enterprises that need risk, controls, and internal audit alongside compliance. Vanta and Drata can also serve larger tech firms, especially for SOC 2 and ISO programs.
Does compliance software include the audit itself?
Usually no. Most platforms prepare evidence, monitor controls, and support the audit process, while an independent auditor performs the audit and issues the report. Thoropass is an exception in offering audit services alongside its platform, subject to contract scope.
How much does compliance audit software cost?
Most vendors in this group quote by headcount, frameworks, and scope, so prices are not published as a simple list. Budget separately for the platform, the independent audit, any pentest, and implementation help.
Sources we checked (8)

Online Jobs is an independent blog about careers, online work, learning new skills and the tools that help people earn. More about us.
Keep reading
All posts
n8n Alternatives
n8n alternatives compared for 2026, with Zapier, Make, Activepieces, and more, covering visual builders, code steps, self-hosting, and pricing models.

ZoomInfo Alternatives
The best ZoomInfo alternatives in 2026, compared on price, free plans, data coverage, and which tool fits small teams or large sales teams best in detail.

Zoom Alternatives for Webinars
Compare Zoom alternatives for webinars in 2026, from browser-based rooms to enterprise events, with prices, attendee limits, features and honest trade-offs.